

New virus infects Android car multimedia centers without the driver noticing
Invasion does not require clicking on links, pendrive or pirated application, and hit equipment of the type that is installed after buying the car in Brazil
By
Eduardo Passos
Published on 2026-09-18 at 12:00 PM
Published on 2026-09-18 at 12:00 PM
Be the first to comment.
Summarize with:
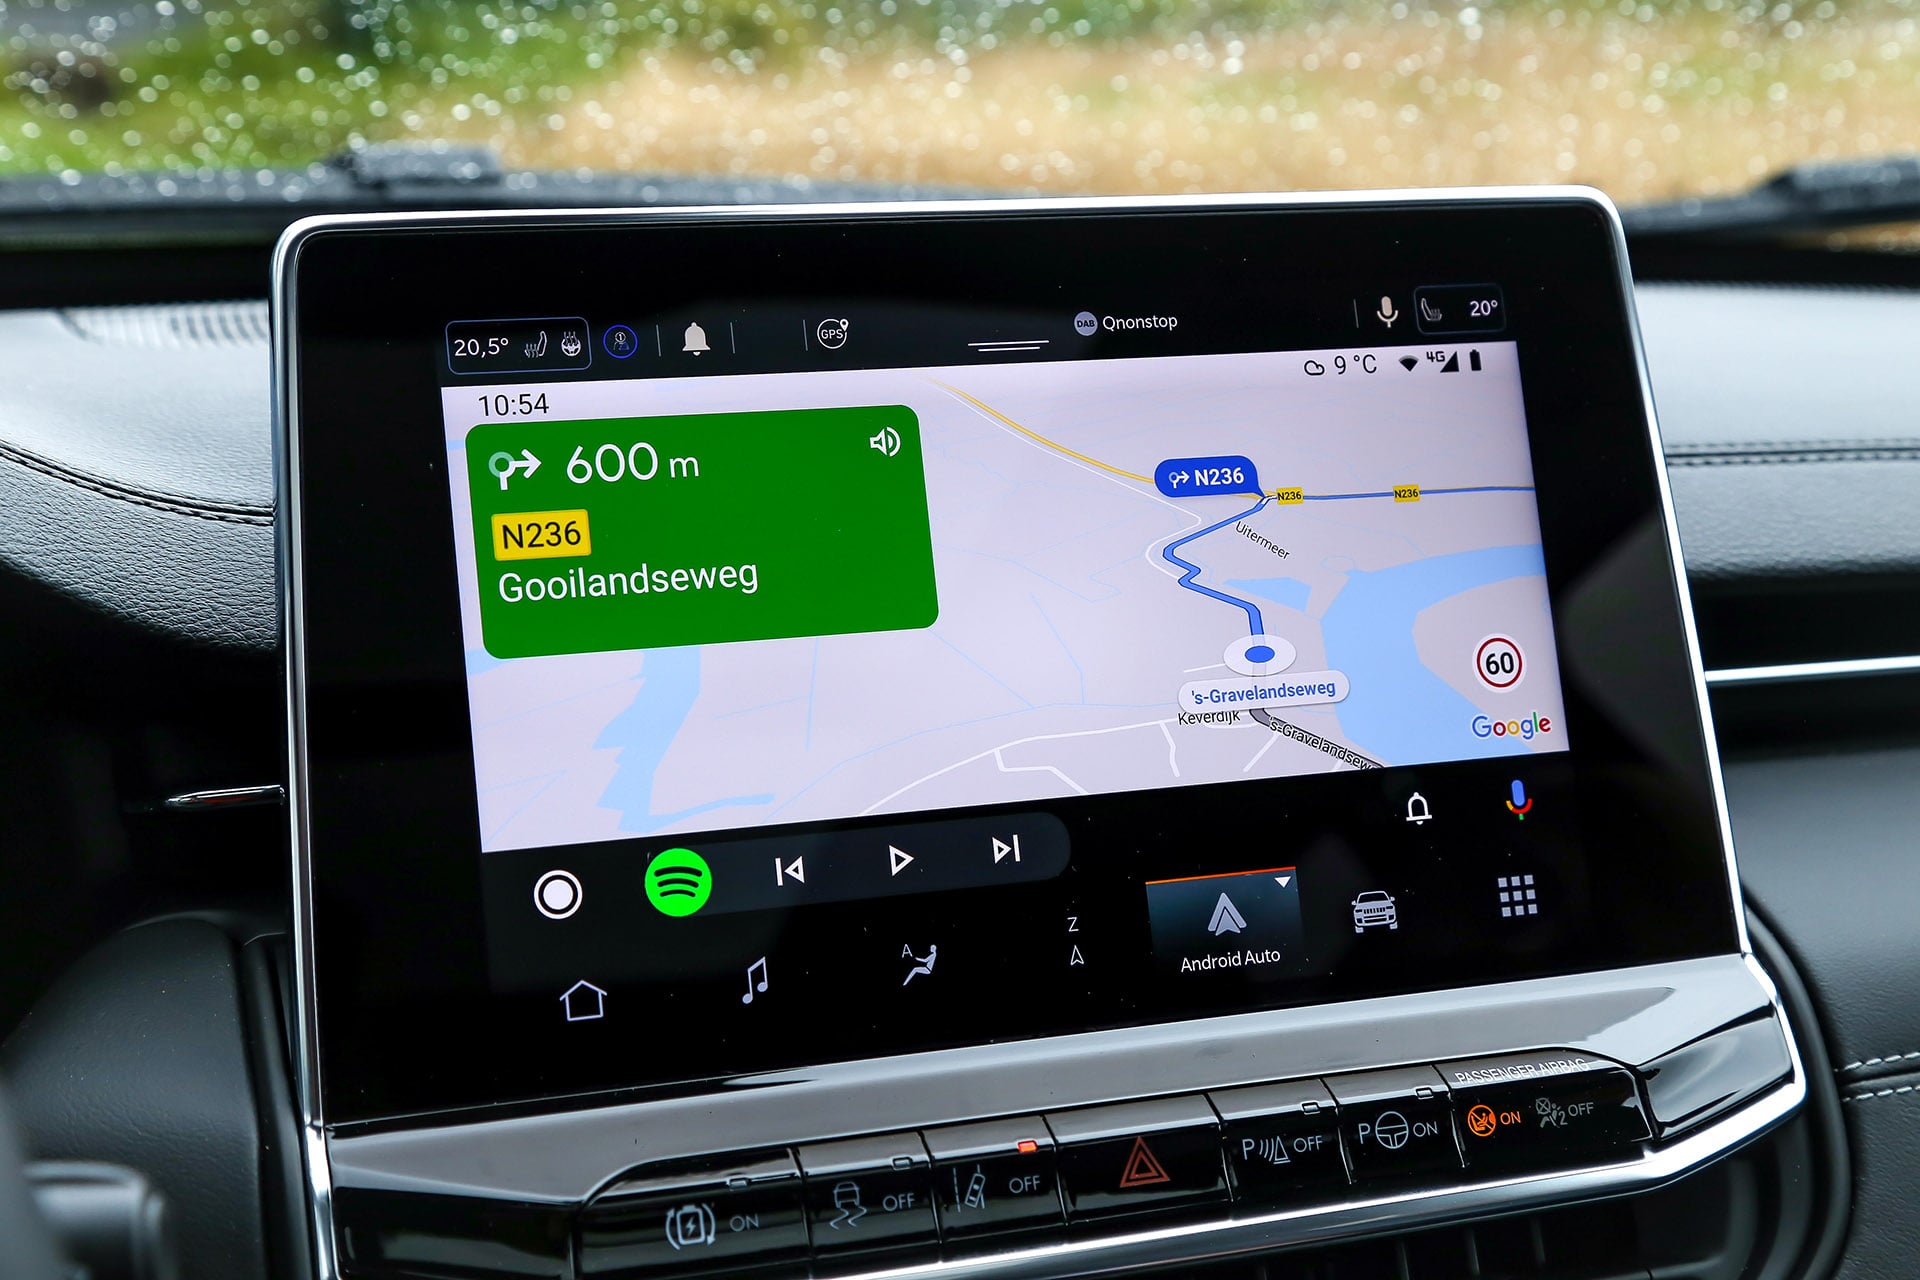
You are a driver aware of cyber risks: you don’t click on suspicious links, you don’t connect unknown USB sticks to your car or use pirated apps. Even so, your car’s multimedia center can become part of a criminal network on the internet.
This is what describes a Kaspersky analysis of a malware campaign created specifically to infect Android multimedia centers.
According to the researchers, the attack abused the device’s own update mechanism, the one that exists precisely to keep the system secure.
Once installed, the malicious program ran in the background, without an icon and without a warning on the screen, and paved the way for other components to be downloaded later.
What the attacker did with your central
The analysis identified functions to collect technical data from the device, such as model, screen resolution, connected Wi-Fi network and MAC address.
The code also practiced advertising fraud and, mainly, transformed the central into a proxy: the traffic of strangers started to travel through the car’s internet connection, integrating the equipment into a botnet, the name given to networks of remotely controlled devices.
The activity was attributed with a high degree of confidence to the criminal group MoYu, associated with the BadBox botnet, already linked to attacks against other connected Android devices.
Less bad that there is no evidence that the attackers took over the vehicle’s steering, brakes or accelerator. The target was the multimedia and its internet connection, not the car’s critical systems.
Kaspersky also did not release a list of affected cars, and having a center with Android or using Android Auto does not mean, in itself, being vulnerable.
Why the case is of interest to the Brazilian
driver The affected centers used software from the Chinese DoFun, a supplier that serves both automakers and equipment installed after the purchase of the car.
This second group is huge in Brazil, where changing the factory radio for a generic multimedia with Android has become customary, often in accessory stores and without any guarantee that the software manufacturer will continue to distribute corrections. Some of these devices have their own connection, including by cell phone chip, which expands the exposure.
DoFun was notified and claimed to have fixed the flaw, which makes updating the system the main protection measure.
It is also worth installing only from official sources, avoiding APKs and alternative stores, checking if the manufacturer still offers security updates, and seeking technical assistance if the center starts to display unexpected ads, crash for no reason, or consume a strange volume of data.
SEE MORE ABOUT

0 Comments
Comments are the sole responsibility of their authors and do not represent the opinion of this site. Comments containing profanity or offensive language will not be published. If you identify anything that violates the terms of use, please report it.